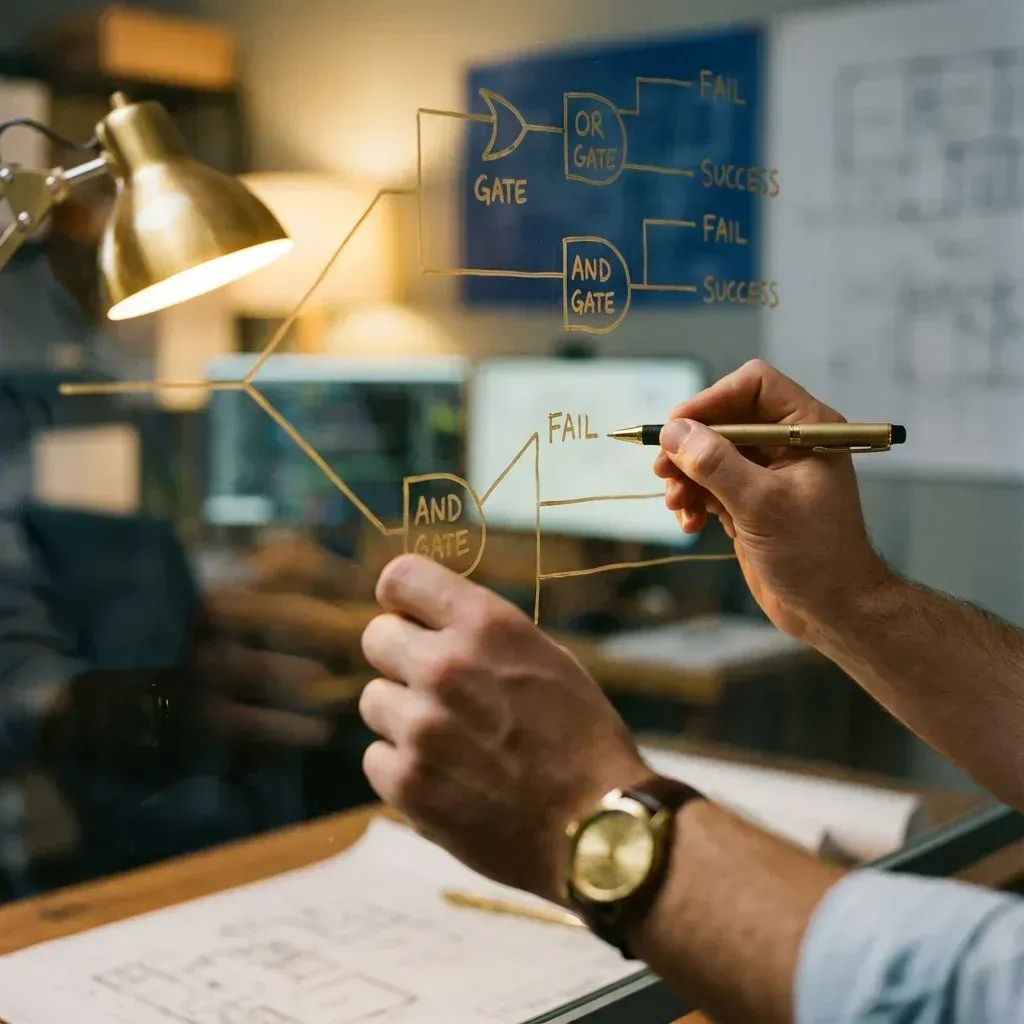
Fault tree analysis starts with an unwanted top event and explores its causes; event tree analysis starts with an initiating event and traces conditional outcomes.
Fault tree analysis (FTA) reasons backward from a defined unwanted top event to combinations of causes. Event tree analysis (ETA) reasons forward from an initiating event through conditional system responses to possible outcomes. The two methods answer different questions and can be used together when the study scope needs both.
Use FTA when you need to examine how a specified system failure or top event can occur. Use ETA when you need to explore how a defined initiating event can develop under different safeguard responses. Neither method alone establishes the completeness of a site risk assessment or proves that safeguards work.
How does fault tree analysis work?
FTA begins with a clearly defined top event, such as loss of containment from a particular system boundary. The analyst then uses logical relationships to represent combinations of equipment failures, human actions and other causes that could lead to that event. An AND gate means the represented combination requires all stated inputs; an OR gate means any stated input can produce the output in that model.
An FTA can be qualitative or quantitative. A probability or frequency calculation requires a defined system boundary, valid event logic, suitable data and explicit treatment of dependencies and uncertainty. A tree diagram by itself is not a root-cause finding, and assigning generic failure rates does not make the result site-specific.
How does event tree analysis work?
ETA starts with a defined initiating event, such as a release or equipment failure. It then traces the possible success or failure of relevant safeguards or conditions and records the resulting outcome sequences. Branches should reflect the scenario, event order and conditional dependencies rather than assume that every safeguard acts independently.
Where the analysis is quantitative, each branch probability needs a stated basis. The sequence frequency depends on the initiating-event frequency and the conditional likelihoods used along that path. An ETA can support consequence and risk work, but the analyst must explain which outcomes, exposure assumptions and endpoints are included.
What is the difference between FTA and ETA?
| Question | Fault tree analysis | Event tree analysis |
|---|---|---|
| Starting point | A defined unwanted top event | A defined initiating event |
| Direction | Backward to possible causes | Forward through conditional events |
| Main question | What combinations could produce this event? | What outcomes can follow this event? |
| Typical structure | Boolean logic such as AND and OR gates | Branches representing event or safeguard responses |
| Quantitative result | Top-event probability or frequency when data and assumptions support it | Outcome-sequence frequencies when branch probabilities are supported |
| Choose a method based on the question, available data and decision. A larger model is not automatically better; include detail when it can change the decision or represent an important dependency. |
Can FTA and ETA be used with BowTie, LOPA or SIL work?
FTA and ETA are formal analysis techniques. A BowTie diagram is a visual way to organise threats, a top event, consequences and barriers. A BowTie can share concepts with fault and event trees, but it does not become a quantitative FTA or ETA simply because its left and right sides resemble those directions.
Layer of Protection Analysis (LOPA) is a separate, scenario-based method. It uses defined initiating-event frequencies and qualifying independent protection layers, along with any relevant conditional modifiers and target criteria under the selected procedure. Do not credit a safeguard as an independent protection layer unless it meets the study's criteria, including independence and auditability. LOPA results depend on the chosen method and data; this article does not set a universal risk-tolerance criterion.
Safety Integrity Level (SIL) requirements apply to safety instrumented functions, not to a whole plant or a generic FTA. IEC 61511 sets lifecycle requirements for process-sector safety instrumented systems; its Part 3 gives guidance for determining required SILs. A risk analysis may inform that lifecycle, but a tree diagram alone does not assign or verify a SIL.
What information should be agreed before the study?
Define the decision, system boundary, operating modes, initiating event or top event, safeguards in scope, data sources, dependencies, uncertainty and required outputs. Ask the study team to show how assumptions affect the result and what the model excludes. For South African major hazard installations, Regulation 10 requires an approved inspection authority to carry out the risk assessment in accordance with SANS 1461. The regulation does not name FTA or ETA as universally mandatory techniques; confirm detailed method requirements with the applicable standard and study scope.
Frequently asked questions
Is fault tree analysis the same as an incident investigation?
No. FTA explores combinations of causes for a defined top event. An incident investigation examines evidence from a specific event and its organisational and technical context. Investigators may use fault-tree logic where it helps answer a scoped question, but a tree does not substitute for collecting and evaluating evidence.
Does event tree analysis prove that a safeguard is effective?
No. ETA can represent a safeguard branch and, with valid data, analyse its effect on outcomes. Effectiveness and branch probabilities need evidence, suitable assumptions and treatment of dependencies.
Which method should I use first?
Start with the decision. If the question is how a particular system can reach an unwanted state, consider FTA. If it is what can follow an initiating event, consider ETA. A competent analyst may use both or another method when the scope requires it.
Does a LOPA result automatically determine the SIL of an instrumented function?
No. SIL determination and verification follow the functional-safety lifecycle and applicable criteria. IEC 61511 provides process-sector requirements; use the applicable standard, site procedure and competent functional-safety review.
Related resources
- Quantitative Risk Analysis guide
- Layer of Protection Analysis explained
- BowTie analysis and barrier health
- South African MHI risk assessment requirements
Sources
- IEC 61025: Fault tree analysis (FTA application guide)
- IEC 62502: Event tree analysis (ETA principles and guidance)
- IEC 61511-1: Safety instrumented systems for the process industry (process-sector SIS lifecycle requirements)
- IEC 61511-3: Guidance for determining required SILs (functional-safety guidance; it does not specify a SIL for each application)
- South African Major Hazard Installation Regulations, 2022, Regulation 10 (AIA/SANS 1461 risk-assessment duty)
MMRisk supports major-hazard and risk-assessment work. Contact our team to discuss a study scope and decision.